HIPAA compliance doesn’t keep a medical website out of the rankings. What it restricts is how that site collects, stores, and shares information about the people who visit it, and several tools SEO teams install without a second thought (analytics platforms, retargeting pixels, chat widgets, lead forms) can quietly cross that line. Handled correctly, compliance work reinforces the same trust signals Google already rewards on healthcare sites. Handled as an afterthought, it turns into a legal and financial liability that forces a practice to rip out tracking infrastructure mid-campaign, sometimes years after a pixel first went live. This guide walks through where HIPAA and medical SEO actually intersect, what changed in the regulatory picture recently, and how to build a compliant SEO program instead of patching one after the fact.
Table of Contents
ToggleWhat HIPAA Actually Governs on a Marketing Website
HIPAA applies to “covered entities” (providers, health plans, and clearinghouses) and their “business associates,” meaning any vendor that creates, receives, maintains, or transmits protected health information (PHI) on the covered entity’s behalf. Three rules matter for a website: the Privacy Rule, which limits how PHI can be used and disclosed; the Security Rule, which sets safeguards for electronic PHI; and the Breach Notification Rule, which requires reporting when PHI is exposed without authorization. That data doesn’t stay confined to a front-end form, either. It flows into the same back-office systems that support your medical billing and coding services, which is exactly why compliance has to be treated as an organization-wide project, not a website-only checklist.
None of this targets keywords, headings, or content topics directly. It targets data: names, contact details, appointment reasons, diagnoses, insurance information, and anything else that can be tied to a specific person’s health status. A blog post explaining a condition isn’t PHI. A form that asks a visitor to describe their symptoms, tied to their name and email, can be.
Where HIPAA Rules and Medical SEO Actually Collide
Analytics platforms and tracking pixels
Standard Google Analytics 4 (GA4) configurations run client-side, meaning data travels straight from a visitor’s browser to Google’s servers before anyone on your team reviews it. GA4 can capture query strings, referral URLs, on-site search terms, and form field data, any of which may include PHI if a patient searches for a condition or fills out an intake form on that page. Google does not offer a business associate agreement for GA4, so once PHI reaches it, you’re out of compliance regardless of intent. The same limitation applies to Meta’s pixel and most out-of-the-box retargeting tags: they’re built for e-commerce attribution, not health data handling.
The OCR bulletin, the court ruling, and what’s actually left of it
In December 2022, the HHS Office for Civil Rights issued a bulletin stating that connecting a visitor’s IP address to a visit to a webpage about specific health conditions could count as an impermissible PHI disclosure, even on public pages that didn’t require a login. OCR revised the bulletin in March 2024 after industry pushback but kept the core position. The American Hospital Association sued, arguing OCR had exceeded its authority, and on June 20, 2024, a federal court agreed, ruling that portion of the bulletin was “promulgated in clear excess of HHS’s authority under HIPAA.” OCR withdrew its appeal that August.
That ruling matters, but it’s narrower than a lot of marketing content suggests. HHS’s own current guidance confirms the court vacated the bulletin specifically where it treated an IP address connected to a visit to an unauthenticated public webpage about a health condition as automatically triggering HIPAA obligations, and the agency notes it’s still evaluating next steps. What the ruling did not touch: the Security Rule still applies in full to actual electronic PHI, authenticated patient portals remain squarely covered, and a tracking tool that captures a name, email, or appointment reason alongside a health topic is still handling PHI. The vacatur removed one aggressive interpretation of a public blog page visit. It didn’t rewrite HIPAA.
One more wrinkle worth knowing: if a tool in your stack isn’t run by a HIPAA covered entity at all, for example a health app or wellness platform sitting outside traditional care delivery, it can still fall under the FTC’s Health Breach Notification Rule, which requires breach reporting independent of anything HHS decides.
Is your medical website leaking data to third-party pixels?
Hidden tracking pixels and unconfigured analytics tags are exposing practices to major state privacy lawsuits and HIPAA vulnerabilities. Let our team map your data layer, audit your tags, and secure your marketing infrastructure.
The bigger legal exposure right now: state privacy lawsuits
Here’s what most coverage of this topic misses: OCR enforcement was never the primary source of pain for healthcare marketers on this issue. State-level privacy and wiretapping statutes have generated far more litigation, and they don’t care what happened to the HHS bulletin. In 2025, a dental services organization agreed to an $18.7 million settlement over claims that Meta and Google tracking pixels on its website shared appointment-booking data with those companies without adequate consent, one of several similar settlements reached by health systems and hospitals around the same pattern: pixels and analytics tags quietly forwarding user behavior to third-party ad platforms. None of those cases turned on the vacated portion of the OCR bulletin. They turned on state consumer-privacy and wiretap laws, which is exactly why the court ruling didn’t make this problem disappear.
Forms, chatbots, and appointment schedulers
Any field that lets a visitor describe symptoms, select a reason for their visit, or upload documents can generate PHI the moment it’s tied to a name or contact method. Chat widgets and AI assistants are a growing risk here, since transcripts often get logged and analyzed by a third-party vendor that has never signed a BAA.
Authenticated portals versus public marketing pages
A patient portal, secure messaging tool, or online scheduling system tied to a specific account carries a different risk profile than your blog. These touchpoints hold real electronic PHI and fall squarely under the Security Rule: access controls, encryption, audit logs, and a signed BAA with every vendor in that stack. Your public-facing content marketing pages carry lower inherent risk, but only if you keep PHI-collecting tools off them.
Reviews, testimonials, and before-and-after content
Patient testimonials and case studies can’t include identifiable health information without a written HIPAA-compliant authorization, and before-and-after photos need the same. This isn’t a reason to skip social proof. It’s a reason to get the paperwork right before you publish it.
Why Compliant Execution Actually Strengthens Medical SEO
Compliance and rankings aren’t pulling in opposite directions. A secure site, a transparent privacy policy, named clinician authorship, and a documented editorial process are exactly the trust signals Google weighs more heavily on health content than on almost any other category, since medical topics fall under its “Your Money or Your Life” classification. A medical SEO strategy that treats data handling as part of the technical foundation, alongside site speed and structured data, tends to hold up better over time than one that treats it as legal’s problem.
There’s also a practical cost to getting this wrong that has nothing to do with fines. When a complaint, breach notice, or class action forces you to strip out tracking pixels and reconfigure analytics on short notice, you lose historical conversion data, break attribution models mid-campaign, and often have to rebuild reporting from scratch. That disruption is a bigger drag on a working SEO and paid media program than the fix would have been if you’d built it correctly from the start.
How to Optimize Your Site for Medical SEO Without Creating HIPAA Risk
Map where PHI can enter your marketing stack
Before changing any tool, walk every page that collects data: contact forms, appointment requests, chat widgets, newsletter signups, and any authenticated section. Note what each field captures and where that data goes next. You can’t fix a leak you haven’t located.
Move analytics server-side or to a HIPAA-eligible platform
Server-side tagging lets you filter identifiers and PHI before data ever leaves your environment, rather than trusting a client-side script to behave. If you need a signed BAA and fully HIPAA-eligible analytics, several platforms now offer that; if you’re staying on GA4 for non-health pages, keep it strictly off any page or form that can capture symptom, condition, or appointment-reason data.
Separate authenticated experiences from public marketing pages
Your scheduling portal, patient messaging tool, and results dashboard belong in a locked-down, BAA-covered environment. Your blog, service pages, and location pages don’t need that same architecture, which is one reason working with a team focused on building a HIPAA-conscious medical website tends to produce a cleaner split between the two.
Build content that never needs PHI to rank
This is the part every competitor article gets right, so it’s worth restating plainly: blog posts, condition explainers, treatment overviews, provider bios, and FAQ pages are fully permissible SEO assets and don’t require a single piece of patient data to perform. The content most medical practices need for organic visibility, informational articles that answer real patient questions, sits entirely outside the compliance risk zone. The risk lives in the tools bolted onto that content, not the content itself.
Use schema markup that doesn’t require patient data
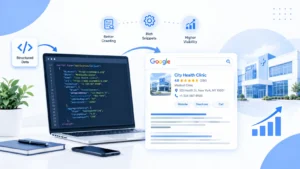
FAQPage, Article, Physician, and MedicalOrganization schema all describe your practice, your content, and your providers using information you already control publicly. None of it requires patient-level data, so there’s no reason schema implementation should ever touch PHI.
Put a BAA in front of every vendor that touches your funnel
Analytics tools, chat widgets, scheduling software, CRM platforms, and marketing automation tools all count as business associates the moment they can access PHI, and each one needs a signed BAA before it goes live, not after an incident.
If your practice is currently vetting new credentialing and software integrations, apply that same BAA-first standard to every marketing tool in your stack.
The same due diligence criteria your team already uses when evaluating credentialing software work just as well for a chat widget or analytics platform.
Compliance Checklist Before You Publish or Launch a Campaign
- Confirm no analytics or ad pixel runs on pages with forms that can capture symptom, diagnosis, or appointment-reason data.
- Verify every vendor touching PHI, from chat widgets to CRM tools, has a signed BAA on file.
- Keep authenticated patient tools (portals, secure messaging) on infrastructure separate from public marketing pages.
- Route analytics through server-side tagging or a HIPAA-eligible platform for any page that could capture PHI.
- Get written, HIPAA-compliant authorization before publishing any testimonial, case study, or before-and-after photo.
- Review your privacy policy to reflect what your site’s tools actually collect, not a generic template.
- Audit existing tags and pixels quarterly. Marketing stacks change faster than compliance reviews usually keep up with.
- Train whoever manages the website and campaigns on what counts as PHI in a marketing context, since most exposure comes from good-faith mistakes, not intentional misuse.
Build a Compliant Medical SEO Strategy That Ranks
You don’t need to risk patient privacy to drive organic traffic. We help healthcare practices scale their visibility through secure technical architectures, optimized content, and risk-free tracking.
Frequently Asked Questions
Does HIPAA compliance hurt medical SEO rankings?
No. HIPAA restricts data handling, not content topics, headings, or keyword usage. Blog posts, service pages, and FAQ content can be fully optimized without touching PHI. The trust signals compliance produces, security, transparency, and clean data practices, tend to support rankings rather than limit them.
Is Google Analytics 4 HIPAA compliant?
Not by default. GA4 doesn’t offer a business associate agreement, and its client-side tracking can capture query strings, form data, and search terms that include PHI. Keep it off any page where patients might submit health information, or route that data through server-side tagging or a HIPAA-eligible analytics platform.
Can a blog post about a medical condition violate HIPAA?
Generally, no. Educational content about a condition, treatment, or procedure isn’t PHI because it isn’t tied to a specific patient. The risk appears when that content sits next to a form, chatbot, or tracking tool that collects identifiable information from the person reading it.
What happened to the HHS bulletin on tracking technologies?
A federal court vacated the portion of the bulletin stating that connecting a visitor’s IP address to a visit to an unauthenticated webpage about a health condition automatically counts as a PHI disclosure. HHS withdrew its appeal in August 2024. The rest of HIPAA’s Privacy, Security, and Breach Notification Rules still apply in full, and state privacy laws have filled much of the enforcement gap the ruling left behind.
Do I need a business associate agreement with my SEO agency?
If that agency’s access, tools, or reporting could touch PHI, yes. If the work is strictly public content, technical SEO, and keyword strategy with no PHI exposure, a BAA may not be required, but confirm that boundary in writing rather than assuming it.
Where to Go From Here
None of this is a reason to slow down a medical SEO program. It’s a reason to build the data layer correctly before you scale traffic to it. Start with the audit: map your forms, check your tags, and confirm your BAAs are current. Everything else, content, schema, technical SEO, builds on top of that foundation without adding risk.